Posts

Windows Registry Forensics

Image
This blog post will cover how registry keys are stored in memory. There are many good tools available to extract windows registry information from memory or dump but it's always good to learn how the information is stored in memory and how these tools are extracting it. Windows Registry (Configuration Manager) in memory is represented using CMHIVE  structure.You can view CMHIVE structure here  https://www.nirsoft.net/kernel_struct/vista/CMHIVE.html . More about Registry structure can be found here  https://binaryforay.blogspot.in/2015/01/registry-hive-basics.html . We can locate CMHIVE structure in memory by scanning pool tag value  CM10 . The pool tag is part of POOL_HEADER ( https://www.nirsoft.net/kernel_struct/vista/POOL_HEADER.html ).The size of POOL_HEADER structure is 8 bytes in 32-bit OS and lies above CMHIVE structure in memory.Below is the result of command ! poolfind <tag> <pooltype>  in windbg where tag is CM10 and pooltype =1...
Memory Forensics : Tracking Process Injection

Image
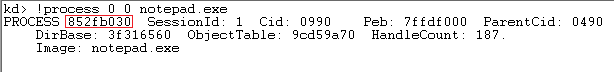
This post describe about process memory internals which allow us to track process injections. Example used below is recent Brazil Malspam (hxxp://malware-traffic-analysis.net/2017/07/07/index.html) which inject DLL  fltLib.dll into process notepad.exe. Attach kernel debugger to infected machine and get information about notepad.exe  Process   object. Process object is represented by EPROCESS structure. VAD (Virtual Address Descriptors) is member of EPROCESS  structure and describes the layout of process memory segments. VADs contain the names of memory-mapped files, the total number of pages in the region, the initial protection (read, write, execute), and several other flags that can tell you a lot about what type of data the regions contain. VAD is a self balancing tree and each node in tree represent one range in process virtual memory.Each node has child in the form of left and right node.A node is represented using MMADDRESS_NODE struct...

PaloAlto CTF 2017 : Binary Challenge 2

Image
The challenge compute flag using time received from NIST Internet Time Servers and then send computed flag to " labytime.com " server for verification. Before forming flag by using time received from  NIST Internet Time Servers the 2nd digit of seconds in received time is set to 0. We have 10 secs to send the computed flag to " labytime.com " server to get correct flag. Re-implemented the logic in python to calculate flag and sending it to " labytime.com " server and reading response to get flag.Below is the python implementation. from rotate import __ROR__ import hashlib import socket import requests c = [0x0C,0x74,0x0C,0x74,0x8D,0x39,0x39,0xED,0x35,0x5D,0x41,0x91,0x39,0x0D,0x15,0x45,0x8D,0x41,0x1D,0x81,0x1D,0x39,0x35,0x31,0x15,0xD9,0x35,0xDD,0x45,0x0C,0x74,0x0C,0x74,0x0C] ror_n = len(c) & 7 decode_str = '' for i in range(0,len(c)):     v = __ROR__((c[i]),2) & 0xFF     #print hex(v)     v = (v ^ len(c))& 0xF...