Posts

FireEye FLARE CTF 2017 : APK Challenge 8
Image
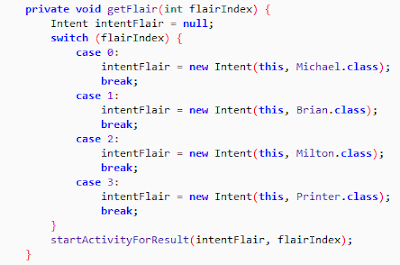
The challenge required decrypting passwords in order to form AES key to decrypt the flag bytes. On decompiling flair.apk file we can see four classes for which we need to decrypt passwords. 1.Michael Class  It was pretty simple password comparison.The password is  MYPRSHE__FTW . 2. Brian Class Password is formed as shown below. String.format("%s_%s%x_%s!", new Object[]{t, y, Integer.valueOf(p), c}); t = (ImageView) findViewById(R.id.pfdu).getTag().toString() y = getApplicationContext().getPackageManager().getApplicationInfo(getApplicationContext().getPackageName(), 128).metaData.getString("vdf") p = (TextView) findViewById(R.id.vcxv).getCurrentTextColor() & SupportMenu.USER_MASK; c = (TextView) findViewById(R.id.vcxv).getText().toString().split(" ")[4]; The Password is  hashtag_covfefe_Fajitas! . 3.Milton Class The password is formed by decrypting a string and taking SHA1 of the decrypted string. Decryption algorithm...

FireEye FLARE CTF 2017 : PEWPEWBOAT Challenge 5

Image
The challenge is about selecting correct coordinates on to the map and advancing to the next stage to get flag. As we advance to next stage, the game print some metadata. After debugging the binary, the logic to calculate co-ordinate can be rewritten. Below is the python implementation of calculating co-ordinate and decrypting metadata for each stage. import binascii key = 0x3B1EE5F6B3D99FF7                #initial key to decrypt metadata. offset = 0x50E0                         #offset of metadata in binary f = open('pewpewboat.exe','rb') for i in range(0,11):     stage = i     v = ((i << 3) + i) << 6     f.seek(offset + v)     mask = '0x'     temp = '0x'     res = []     metadata = []     for i in range(0,0x240):         key = ((key * 0x41c64e6d) +...

Samsung CTF : Chicken or Egg Reversing Challenge

Image
 The CTF is over but i really enjoyed solving the challenge (https://sctf.codeground.org/ctf/prob).The challenge is to decrypt flag.enc. This is another APK + JNI (Java Native Interface) kind of challenge similar to the one in Google CTF 2017 (http://shasaurabh.blogspot.com/2017/07/google-ctf-2017-android-re-challenge.html). Challenge can be divided into three parts. 1.Android application (application) loading Native Library 2.Native Library decrypts DEX file in memory. 3.Using Reflection to call methods of decrypted DEX file in step 2. 1. Android application loading Native Library OnClick() method of MainActivity class calls constructor of Crypt class. Calling constructor of Crypt class results in loading of Native library ( libegg.so ) which is ELF for ARM. Constructor of Crypt class calls crackEgg method implemented in native library. 2.Native Library decrypts DEX file in memory. The native library reads the encrypted DEX file stor...

Windows Registry Forensics

Image
This blog post will cover how registry keys are stored in memory. There are many good tools available to extract windows registry information from memory or dump but it's always good to learn how the information is stored in memory and how these tools are extracting it. Windows Registry (Configuration Manager) in memory is represented using CMHIVE  structure.You can view CMHIVE structure here  https://www.nirsoft.net/kernel_struct/vista/CMHIVE.html . More about Registry structure can be found here  https://binaryforay.blogspot.in/2015/01/registry-hive-basics.html . We can locate CMHIVE structure in memory by scanning pool tag value  CM10 . The pool tag is part of POOL_HEADER ( https://www.nirsoft.net/kernel_struct/vista/POOL_HEADER.html ).The size of POOL_HEADER structure is 8 bytes in 32-bit OS and lies above CMHIVE structure in memory.Below is the result of command ! poolfind <tag> <pooltype>  in windbg where tag is CM10 and pooltype =1...